Typosquatting and Lookalike Domains: The Monitoring Guide
Most brands look for copies the same way: think of the obvious variations of their name, check whether those are registered, and move on. That finds the names you can imagine. It cannot find the ones you cannot, and those are the majority.
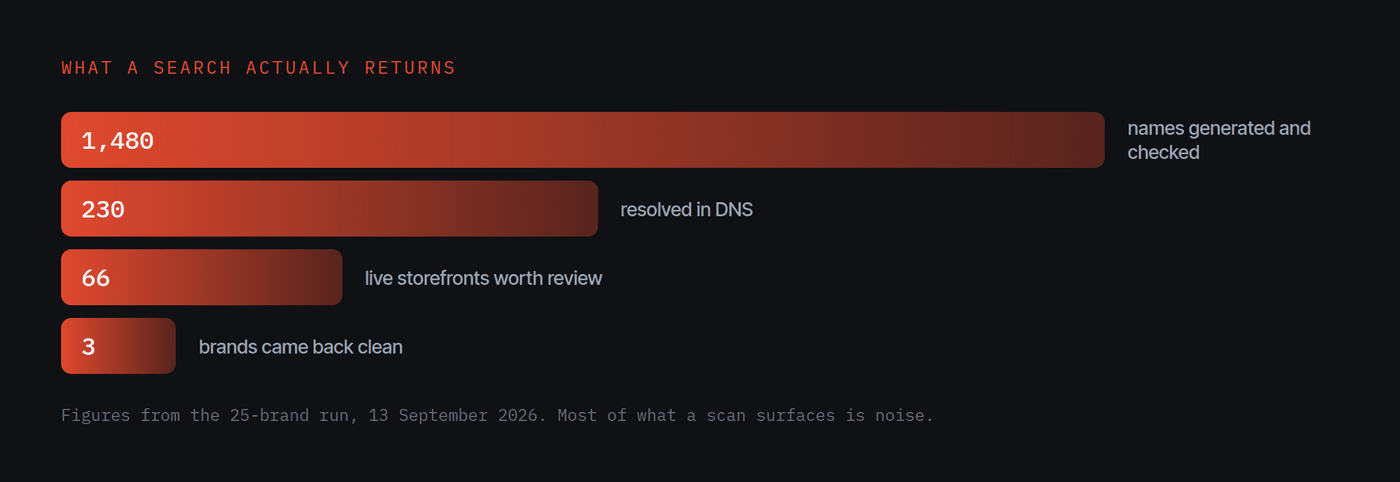
Search public certificate transparency logs at crt.sh for your brand name with wildcards, as %yourbrand%. Any site serving HTTPS must publish its name in those logs before it goes live, so they list names that actually exist rather than variations you guessed. Most matches are noise and have to be filtered before they mean anything.
There is a better source, it is public, and it is free.
Why permutation lists miss most of it
A typosquatting checker starts with your domain and generates variations: a doubled letter, a missing letter, a swapped pair, a different top level domain. Then it checks which of those resolve.
The method is sound and you should run it. Its limit is structural: the list is made of names you generated, so it can only ever contain names that fit your idea of a copy. Real ones often do not. A store selling copies of a brand called Vanterra might sit on vanterra-outlet.shop, which a generator will catch, but it is just as likely to sit on something a generator would never produce, because the operator was not trying to look like a typo. They were trying to look like an official outlet.
The better source: certificate transparency
Any site that serves HTTPS needs a TLS certificate. Since certificate transparency became a practical requirement, issuing a certificate means writing the domain name into a public, append-only log that anyone can read.
The system exists for a security reason: so that nobody can quietly issue a certificate for your domain without it being noticed. The side effect is the useful part here.
A copy of your store cannot go live on HTTPS without announcing its name in public first. And it has to be on HTTPS, because a browser warning on the padlock would cost it the sale it exists to steal.
So instead of guessing names and checking whether they exist, you read a list of names that do exist, and look for yours inside it.
How to search the logs
The most direct public search is crt.sh, run by Sectigo. It is plain and it is free.
- Go to crt.sh and search for your brand name with a wildcard on both sides, in the form
%yourbrand%. The percent signs are wildcards, so this finds any certificate whose domain contains your brand name anywhere. - Sort by the logged date, newest first. Recent entries are the ones that matter.
- Ignore your own certificates, and your certificate provider's. If you are on Shopify, you will see a lot of entries for your own shop and for Shopify's infrastructure. That is expected.
- What is left is the list worth looking at.
Two refinements that make a real difference:
- Search for fragments, not the whole name. If your brand is Vanterra, search
%vanterr%too. An operator who drops or doubles a letter will not match the full string. - Search your product names. Brands forget this one. A store copying your catalogue often puts a hero product name in the domain rather than the brand name.
Most of what you find is noise, and that is normal
This is the part the method usually skips, and it is the part that decides whether the exercise is useful or just alarming.
A large majority of matches will be:
- Parked pages and domains for sale. Registered speculatively, serving an advertising page, doing nothing to you.
- Dead hosts. A certificate was issued and nothing was ever put behind it.
- Unrelated businesses. A company that has traded under a similar name for twenty years is not a copy of you. Check the registration date. A domain that predates your brand cannot be copying it.
- Your own stores. Regional storefronts, staging sites and old campaign domains all look exactly like suspects in a list of names.
Work out which of these each match is before you do anything else. The order matters: a name that looks like yours is not evidence of anything by itself, and treating it as evidence is how a brand ends up sending a notice to a legitimate business.
What actually makes a match worth acting on
One signal is never enough. What turns a look-alike name into something worth a report is a combination:
- The domain is young. Registered weeks ago, selling a brand that has existed for years.
- It serves your images. Check the page source. If the product images load from your own content delivery network, the store is not even hosting its own copies. That one is very hard to explain innocently.
- The text is yours. Your page title, your product descriptions, sometimes including a typo you fixed months ago.
- The policy pages are missing or broken. Refund, terms and shipping pages that error, and no contact address anywhere.
A young domain reusing your page title has an innocent explanation. A young domain pulling image files off your own CDN does not have many.
The limit of doing it by hand
This method works and you should try it today. Its problem is not accuracy, it is cadence.
A store built to copy a brand is typically live within days of the domain being registered and gone within months. A check you run once a quarter will mostly find the wreckage of stores that already took your customers. To catch them while it matters, the search has to run on a schedule and something has to filter the noise before it reaches you, or you stop reading the results within a fortnight.
That is the entire reason automated monitoring exists for this. But the method underneath it is the one above, it is public, and nobody should be charging you for the knowledge of it.
Catch them even earlier: newly registered domains
Certificate transparency catches a copy when it switches on HTTPS, which is usually within a day of going live. One source can be earlier still: the registration itself. Every new domain in a generic top-level domain like .com or .org is written into that registry's zone file, and ICANN's Centralized Zone Data Service lets an approved requester download those zone files daily. Comparing one day's file against the last gives you every domain registered in the previous 24 hours, and filtering that list for names that contain your brand surfaces a lookalike the day it is registered, sometimes before it has a certificate or a single page.
Newly-registered-domain feeds built on this data are how monitoring services catch a copy at registration rather than at launch. The trade-off is volume: millions of domains are registered a day, so the filtering matters even more than it does with certificate logs. It is the same principle as the method above, one step earlier in the timeline, and the same noise problem in a larger form.
Watch names, not complaints
Whichever source you use, the point is to be ahead of the operation rather than behind it. For how a copy actually gets built and sold, see how store cloners actually work. When you find one, the first 24 hours guide has the order to work in, how to take down a fake website covers the routes and costs, and how to find fake copies of your website rounds out the manual checks.
Have it watched for you
Katcher's free imposter scan runs this search for you and shows you the evidence for each match, with no card and no call. It is newer than the enterprise tools and has a smaller takedown track record, but catching a lookalike early is exactly what it is built for.
About the author
Davis Paipa is the founder of Katcher and of Libautech, and has spent five years building on Shopify. He wrote the method out in full because it is public, and nobody should be charging you for the knowledge of it.
Questions
What is certificate transparency?
A public, append-only record of every TLS certificate issued by a participating authority. It exists so that a certificate cannot be issued for a domain in secret. The side effect useful to a brand is that a site cannot go live on HTTPS without its name appearing in a public log first.
Why is this better than a typosquatting checker?
A permutation tool generates variations you already thought of, then checks whether they resolve. It cannot find a name you would never have guessed. Certificate logs work the other way around: they list names that actually exist, so you search what is real rather than what you imagined.
Is searching certificate logs legal?
Yes. The logs are public by design, and reading them is their purpose. You are not accessing anyone's systems, you are reading a published record.
How often should I check?
A domain registered to copy a brand is usually live within days and gone within months, so a monthly check will miss most of them. Weekly catches most, daily catches nearly all of them while they still matter.
What do I do with a match?
Nothing, at first. Most matches are noise: parked pages, domains for sale, dead hosts, unrelated businesses, and your own regional stores. Check whether it is live and what it serves before treating it as anything. A name that looks like yours is not evidence of anything on its own.
What is the best typosquatting monitoring tool?
The best approach is not a single tool but two public data sources run on a schedule: certificate transparency logs, which list a site's name when it switches on HTTPS, and newly-registered-domain feeds built on ICANN zone files, which list a domain the day it is registered. A typosquatting checker that only permutes your name misses the majority of real copies, because operators register names that read as official outlets rather than as typos. Any tool worth paying for is filtering those two feeds for you.
Is there a lookalike domain monitoring service?
Yes, several, and what they do underneath is read certificate transparency logs and newly-registered-domain feeds, filter out the noise, and alert you to names that look like yours. The value is the cadence and the filtering, not secret data: the sources are public. Katcher runs this for Shopify brands as part of its free scan, though it is newer than the enterprise domain-monitoring vendors and has a smaller takedown track record.
Someone registered a domain similar to my brand. What should I do?
Do not act on the name alone, because a similar name is not evidence of anything by itself. Check the registration date, whether the site serves your product images from your own content delivery network, whether the text is yours, and whether the policy pages are missing or broken. A young domain pulling your image files is hard to explain innocently; an unrelated business that has traded under a similar name for years is not a copy. Confirm before you send anything, so you do not file against a legitimate business.